Encrypted overlay filesystem in Go for keeping files in a local encrypted directory
- Stars4.6k
- Forks299
- Open Issues66
MIT
- Go
- Shell
- C
About gocryptfs
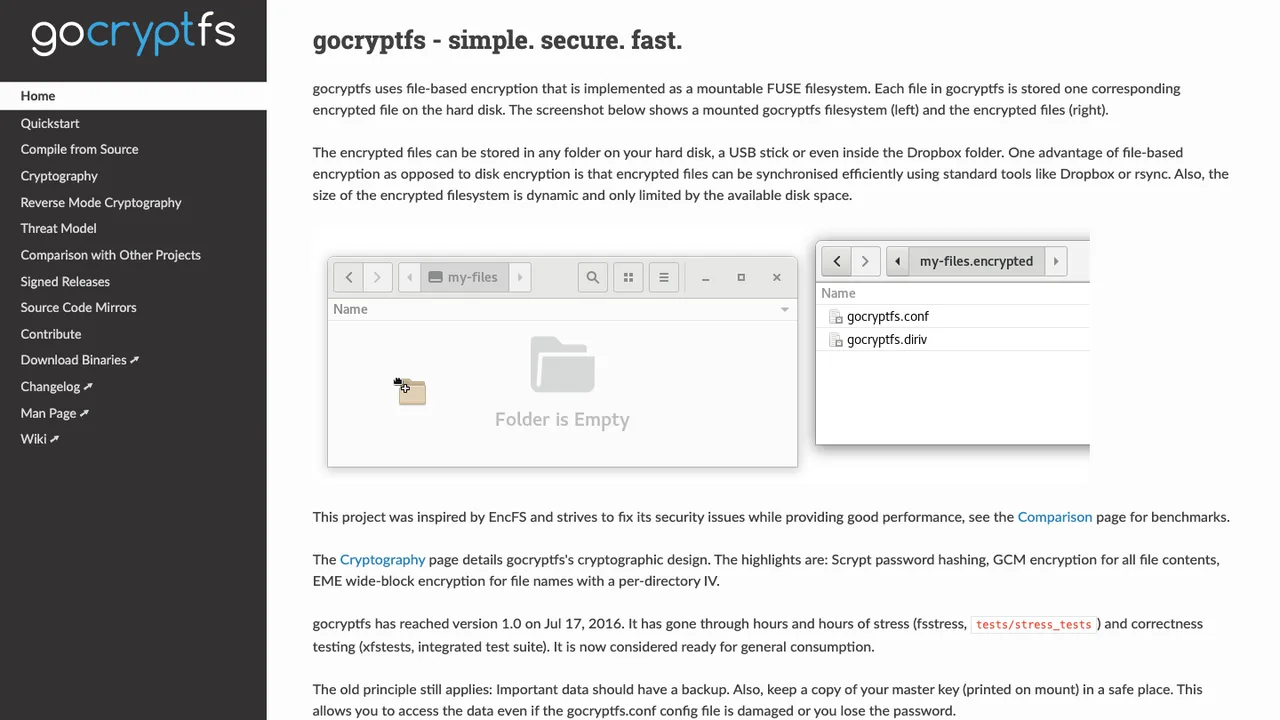
gocryptfs is an encrypted overlay filesystem for Linux and macOS. It keeps encrypted data in one directory and exposes the decrypted files through a separate mounted directory, so your file contents and file names stay encrypted at rest while you read and write them normally.
Built on FUSE and the go-fuse library, it adds a reverse mode that presents an encrypted view of an existing plaintext directory, which is handy for encrypted backups. Filenames are protected with per-directory IVs, content uses AES-GCM or XChaCha20-Poly1305, and a stable command-line ABI lets you call it safely from your own apps and scripts.
Linux is the native platform, with beta-quality macOS support. On CPUs without AES acceleration, gocryptfs can route crypto through OpenSSL via a thin wrapper for a large speedup.
Key features
- Mounted plaintext view over an encrypted directory
- Reverse mode for encrypting existing plain directories
- Stable CLI ABI for apps and scripts
- OpenSSL crypto backend option on CPUs without AES-NI
- Precompiled binaries for x86_64 Linux
Details
- First released
- 2015
- Platforms
- Linux · macOS
- Deployment
- offline-first
- Filesystem
- FUSE overlay filesystem
- Ciphers
- AES-GCM · XChaCha20-Poly1305
- Crypto backend
- Go stdlib or OpenSSL